Pittsburgh's Top Privacy Law Attorneys
Ellis & Patterson helps businesses understand those obligations, meet them, and respond with confidence when something goes wrong.
Your data practices are making promises. We make sure you can keep them.
A few years ago, a privacy policy and a cookie banner were enough for most companies. Today, a growing number of states have their own comprehensive privacy laws, regulators are actively enforcing them, and plaintiffs’ attorneys are filing claims over tracking pixels, biometric data, and chat tools. The rules differ by state, by industry, and by the type of data you collect.
We translate that complexity into clear decisions your business can act on.
Areas of Focus
State Privacy Law Compliance
Each state has different thresholds, consumer rights, and requirements. We determine which laws apply to you and build one coordinated program rather than a patchwork of separate fixes.
GDPR and International Data Transfers
If you serve customers in the European Union or United Kingdom, or move data across borders, we help you establish a lawful basis for processing, manage transfer mechanisms, and prepare for data subject requests.
Health Data and HIPAA
For healthcare organizations, health technology companies, and their vendors, we advise on HIPAA obligations, business associate agreements, and the growing number of state laws that protect consumer health data outside of HIPAA.
Financial Data
We help banks, lenders, and fintech companies meet their obligations under the Gramm-Leach-Bliley Act and related state regulations.
Children’s and Student Privacy
Businesses that collect information from children or students face some of the strictest rules in privacy law. We advise on COPPA, student data laws, and age-appropriate design requirements.
AI Governance
We help businesses evaluate AI vendors, assess automated decision-making, draft internal use policies, and prepare for emerging AI regulations in the United States and abroad.
Contact Now
Get support from one of our trusted attorneys within 24 hours.
The Team
Eleanor Ellis
Founding Partner
Eleanor leads the firm’s privacy compliance practice and advises technology and healthcare companies on building data programs that scale. She holds the CIPP/US and CIPM certifications.
Marcus Patterson
Founding Partner
Marcus guides businesses through data breaches from the first phone call to the final notification. He coordinates forensic investigations, regulator communication, and insurance claims.
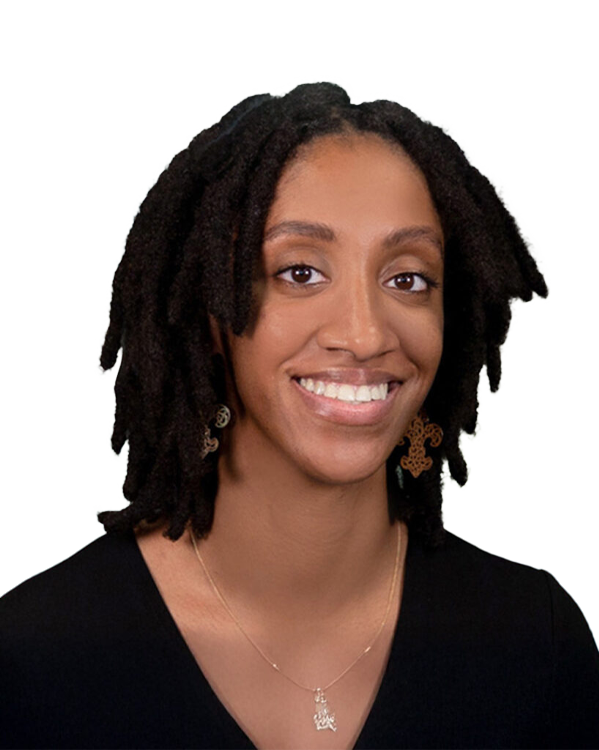
Sofia Marchetti
Associate, AI and Emerging Technology
Sofia helps clients evaluate AI vendors, draft internal use policies, and prepare for new regulations governing automated decision-making.
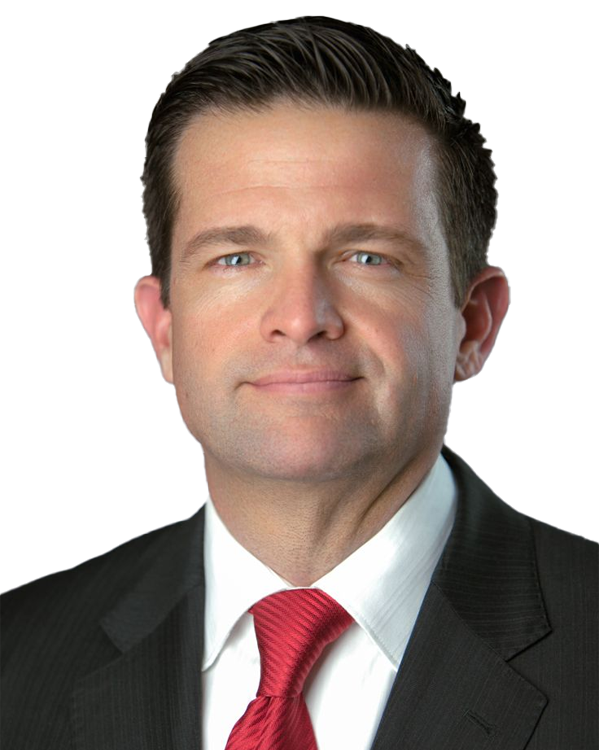
James Okafor
Associate, Health and Financial Data
James advises healthcare organizations and financial services companies on HIPAA, the Gramm-Leach-Bliley Act, and state consumer health data laws.
In the News
Eleanor Ellis Discusses the Wave of New State Privacy Laws
Founding Partner Eleanor Whitfield explained why businesses operating in multiple states are struggling to keep up with conflicting privacy requirements, and how a single coordinated program can reduce both cost and risk.
Marcus Patterson on Why Breach Response Plans Fail
Founding Partner Marcus Patterson shared the most common mistakes companies make after discovering a data incident, including delayed notifications and public statements made before the facts are known.
Ellis & Patterson Named Among Leading Privacy Practices in the Region
Ellis & Patterson was recognized for its work helping technology, healthcare, and financial services companies build privacy programs that hold up under regulatory scrutiny.
Frequently Asked Questions
Does my business need to comply with state privacy laws?
It depends on where your customers live, how much personal information you process, and how much revenue you generate from it. Many businesses are surprised to learn they meet the thresholds. A consultation can answer this quickly.
We are a small company. Do these laws really apply to us?
Some state laws apply only to larger businesses, but others, along with laws covering health data, biometric data, and children’s information, can apply regardless of company size.
Is a privacy policy enough?
No. A privacy policy describes your practices. Compliance requires that your practices actually match what the policy says, along with processes for handling consumer requests, vendor contracts, and security measures.
What should we do if we think we had a data breach?
Contact a privacy attorney before making public statements or sending notifications. Involving counsel early can help protect the investigation under attorney-client privilege and ensures notifications meet every applicable deadline.
Can you work with our in-house legal team?
Yes. We frequently support in-house counsel as an extension of their team, handling specialized privacy matters or providing additional capacity during major projects.
How do you charge for your services?
We offer project-based pricing for compliance programs and assessments, monthly arrangements for ongoing counsel, and hourly billing for incident response and litigation. We discuss fees openly before any work begins.